Lior Levy
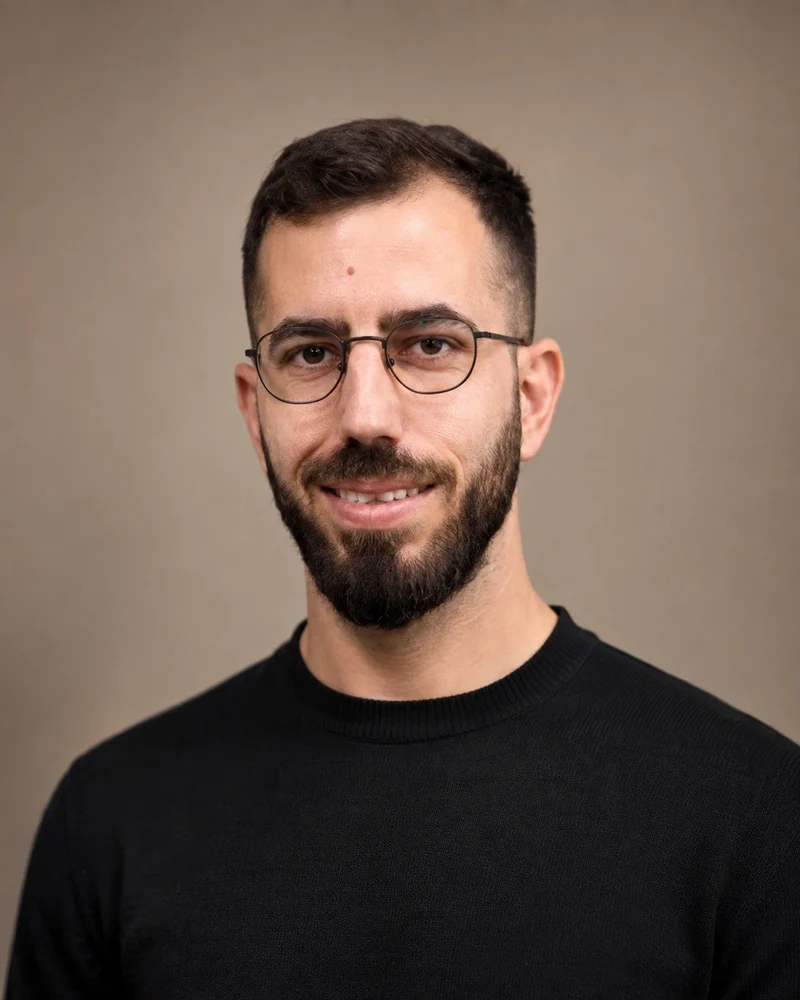
I serve as SrvIT's CISO and DPO, responsible for making sure our clients' data is protected all the way through: how it is stored, who is allowed to access it, which protections are in place, and how we meet the legal and regulatory requirements for privacy and information security.
I come from the practical side of the IT world, with years of experience as a systems administrator and IT systems manager. Before joining SrvIT I managed computing infrastructure, enterprise systems and security equipment at a large technology organization.
That background lets me connect the demands of information security with the actual work - not only defining what needs to be done, but understanding how to implement the protections correctly, efficiently and practically, without burdening staff or paralysing the client's operation.
To me, good information security is not just procedures written in a document. It has to be part of the day-to-day work: from managing permissions and access to data, through protecting the systems, to training staff and raising awareness.
My goal is to make sure the protections don't exist only to satisfy a requirement, but actually work when it matters.
My background
I started out on the technical side of IT - managing computer systems, infrastructure and security at a large technology-mobility company. There I was responsible for servers, networks and endpoint equipment, and for the organization's information-security stack, including Fortinet firewalls and endpoint protection.
That work taught me that real information security starts with control over the details - who gets a permission, how the network is built, and what happens when something goes wrong. I built my technical foundation back in high school, in an electronics and computers track, and from there went deeper into information security and data protection, through to the CISO and DPO role.
What a CISO and DPO do
Every business that handles data - about customers, employees or suppliers - needs someone responsible for protecting it. As CISO I set how the data is secured: permissions and access, network and endpoint protection, backups, and spotting risks before they become an incident.
As DPO I am responsible for the privacy side - that the organization meets the requirements of the privacy-protection law, including Amendment 13, and that there is a clear address for any question on the matter. The two roles complement each other: good security protects the data, and data protection makes sure it is collected and used the way it should be.
How we protect your data
Information security does not rest on a single product. We work in layers - a firewall and endpoint protection, orderly permission management, backups that are tested, and monitoring of what happens on the network. If one layer fails, there are more behind it.
The most important part is actually the people. A large share of incidents starts with human error - clicking a link, a weak password. So I also invest in training and awareness, so the client's team is the first layer of defense, not the weak link.
What sits with me
The areas where I'm responsible for our clients' information security and privacy.
Want to know your data is genuinely protected?
We would be glad to tell you how we secure data and protect privacy for businesses. Leave your details and we will get back to you.